Blog
How SMBs Can Prepare for Customer Security Reviews Without Slowing Down Sales
A promising deal can lose momentum when a prospect sends over a long security questionnaire and asks for policies, test results, and evidence that vulnerabilities were fixed. For a growing business, the same people supporting customers, managing technology, or closing the deal may also have to track down the answers. Security can quickly become a sales bottleneck.
The goal is not to predict every question. It is to build a repeatable process for answering common ones quickly, backing those answers with current evidence, and escalating exceptions to the right person. For cybersecurity for small businesses, that preparation can make customer security reviews far less disruptive.
What do customer security reviews usually ask you to prove?
Security questionnaires vary by customer, industry, and the data or systems involved. But most are trying to determine whether they can trust you to manage their risk responsibly.
Common security questionnaire examples may ask whether you:
Use multifactor authentication and appropriate access controls
Encrypt sensitive data in transit and at rest
Have documented incident response, backup, and recovery processes
Manage third-party and cloud security risks
Conduct vulnerability analysis and penetration testing
Track vulnerabilities through remediation
Customers may also ask for supporting evidence, such as policies, compliance documentation, architecture information, or a recent penetration testing report. The more of that material you have to find from scratch, the longer the review can take.
How can you prepare before a security questionnaire arrives?
Treat security review readiness like any other repeatable sales process. Build the basic materials once, assign ownership, and keep them current.
Identify the questions you’re likely to get.
Review past security questionnaires and customer requirements. Identify recurring questions around access controls, encryption, incident response, backups, vulnerability management, penetration testing, and compliance.Build a library of approved answers.
Create standard responses for questions that come up repeatedly. Have the appropriate security, legal, or compliance owner approve them so sales teams aren’t drafting answers from scratch or making unsupported claims.Organize the evidence behind those answers.
Keep frequently requested documents in one controlled location, including policies, compliance documentation, business continuity information, pen test reports or summaries, and remediation evidence.Assign owners and escalation paths.
Decide who can answer routine questions and who handles technical, contractual, or customer-specific requests. Sales should know where to send exceptions.Keep everything current.
Review approved answers and evidence regularly. Update them when your technology, vendors, policies, testing, or compliance status changes.
How can you automate vendor security questionnaires?
Automation can reduce repetitive work, but it works best when you already have approved answers and current evidence.
Some software is designed specifically to speed up customer security reviews. Instead of starting from scratch, it can store approved responses and documents, match new questions to information you’ve already provided, flag gaps, route unfamiliar questions, and track deadlines.
Automation should support your review process, not replace it. Customer-specific requirements, unusual technical questions, and contractual commitments still need human judgment. Your answers and evidence must also stay current as your systems, vendors, policies, and security practices change.
What is the primary goal of penetration testing?
Penetration testing identifies and validates exploitable weaknesses before attackers can use them. For a customer review, it also shows that you test your defenses and act on the results.
When customers ask about vulnerability analysis and penetration testing, the two provide different levels of insight. Automated analysis identifies known weaknesses, while expert-led penetration testing determines whether they can be exploited, how they may form an attack path, and the potential business impact.
A penetration testing report can help demonstrate what was tested, what was found, and how issues were prioritized. Depending on the customer and sensitivity of the findings, you may provide an executive summary, attestation, or appropriately redacted report rather than distributing detailed technical findings broadly.
Scope matters too. A customer may care most about the internet-facing systems handling its data, while a broader requirement may call for internal and external testing. Our guide to internal vs. external pen testing explains how to match the test to the systems, attack paths, and evidence required.
When comparing pen testing companies, look beyond who can deliver a report. Ask whether the provider can scope testing around your highest-risk systems, explain findings clearly, support remediation, and help verify that important fixes worked.
How can technology streamline security reviews?
Questionnaire automation is only one piece. The underlying evidence also needs to stay organized and current.
Use technology to centralize security information, track remediation, maintain document versions, and control access to sensitive evidence. That reduces manual handoffs every time a prospect asks you to prove a security claim.
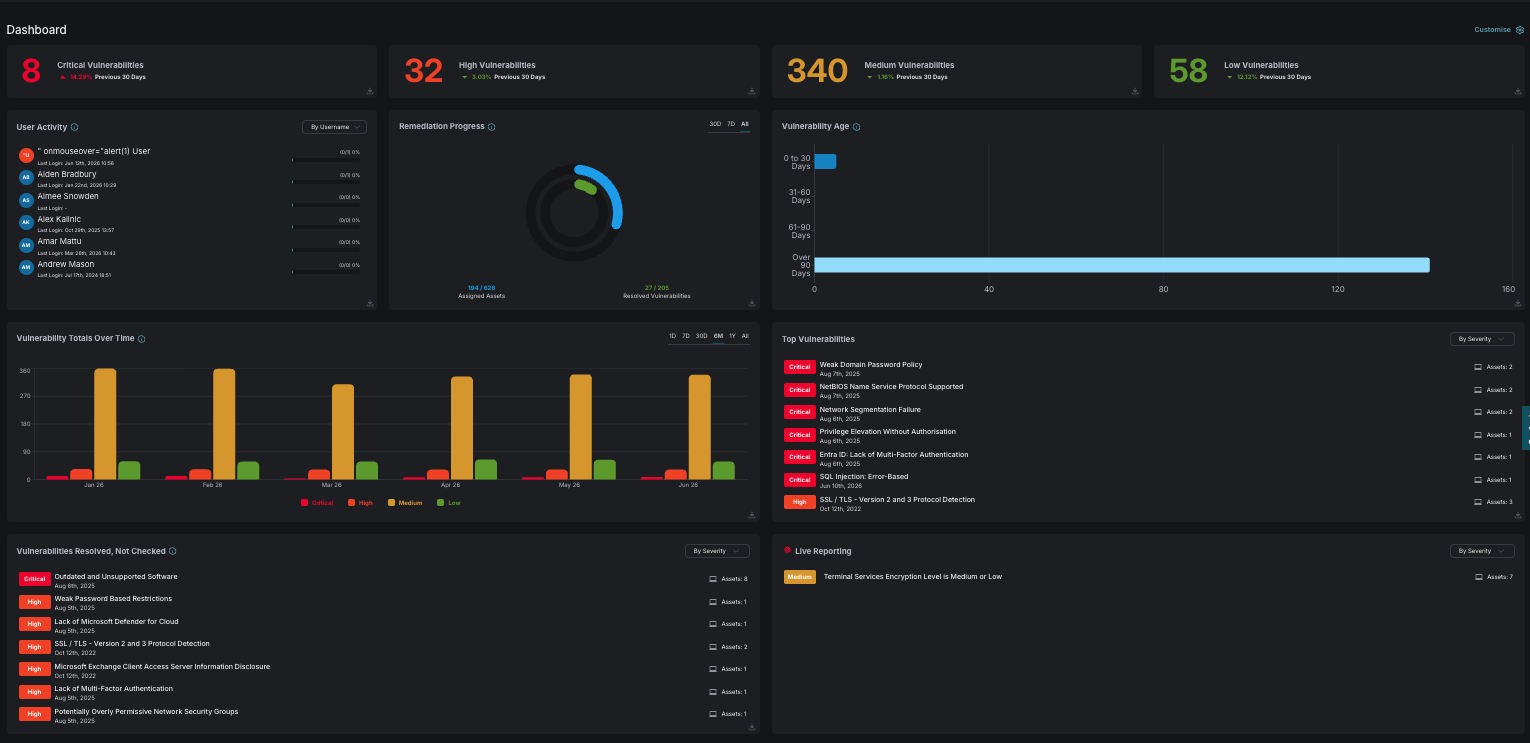
WorkNest takes that approach to penetration testing. Our GuardNest platform centralizes findings, remediation tracking, and reporting, so your team can see what remains open and maintain evidence of progress rather than rebuilding the story when a customer review begins.
GuardNest does not replace a security questionnaire tool. It helps make the vulnerability and testing portion of the review easier to support with current information.
Make security review readiness part of sales readiness
A customer security review should not force you to choose between responding quickly and responding accurately.
Build an approved evidence library, standardize recurring answers, automate routing and reuse, and keep your testing and remediation evidence current. Then your team can spend its time on the questions that actually require judgment instead of recreating basic proof.
WorkNest helps growing organizations turn security findings into fixes and credible evidence without unnecessary enterprise complexity. Talk with one of our experts today.
Why teams love us
From robust threat defence to dependable regulatory assurance, our cybersecurity service helps organisations stay resilient, safeguard their data, and concentrate on what truly drives their success.
We’ve always been very impressed with the cyber security services WorkNest provide us. Their professional approach, knowledge and flexibility have ensured they have become a key trusted partner in our supply chain.

Paymentsense
Founder
WorkNest Secure delivered a highly professional and thorough incident response service. Their team’s technical knowledge, attention to detail, and clear communication throughout the process made a complex area easy to navigate. The quality of the analysis and final reporting gave us real assurance and added value to our internal security efforts, minimising the impact to the business.
Shoezone
Head of IT
WorkNest Secure perform Web Application and Infrastructure Penetration Testing for Pharmacy2U. They are always professional to engage with, provide an excellent level of service, and the addition of GuardNest makes receiving and interrogating the results of the service very easy indeed.
We look forward to working with them in the future and trust the work they deliver.
Pharmacy2U
Founder
WorkNest Secure stand out in the field of penetration testing due to the skillset of people they have working there. We undertook a complex bespoke pentest with them, which required a lot of pre-work in order to make sure it was scoped correctly, and they took the time to come onsite to make sure all was correct prior to commencing.
From my experience with them, they are very intelligent people with a deep understanding of the security landscape, and we will continue to use them for future testing requirements.
Interactive Investor
Information Security Manager