You're viewing this page from our UK site — a US version isn't available yet. Go to our US site
WorkNest Secure
Cyber Essentials Certification
Achieve certification with confidence and ease. Contact us today for expert-led, hands-on support tailored to your needs.
We are an official Cyber Essentials Certification body
We are an official Cyber Essentials Certification body
We are an official Cyber Essentials Certification body
That means we know exactly what it takes to get you certified.
We help you achieve Cyber Essentials and Cyber Essentials Plus certification with an expert-led information security consultancy, flexible packages, and hands-on support tailored to your organisation's size and needs.
That means we know exactly what it takes to get you certified.
We help you achieve Cyber Essentials and Cyber Essentials Plus certification with an expert-led information security consultancy, flexible packages, and hands-on support tailored to your organisation's size and needs.
Cost-Effective Certification
Cyber Essentials Packages
Cyber Essentials Plus
What are Cyber Essentials and Cyber Essentials Plus?
They're government-backed certifications that set a strong cyber security baseline, helping organisations like yours operate securely. It's a requirement for many government and public-sector contracts to gain certification.
Through a self-assessed questionnaire, it demonstrates that you have the five key technical controls in place:
Access controls
Firewalls
Malware protection
Secure configuration
Software updates
Cyber Essentials Plus
Cyber Essentials Plus builds on everything in Cyber Essentials by offering an independent technical audit that verifies all claims made in the self-assessment.
It costs more, but its added security controls can unlock more opportunities, as it is held in higher regard because much of the process is handled by the Certification Body.

Why WorkNest for Cyber Essentials support?
Achieving certification doesn't have to be complicated. We're here to make it easier.

Certified assessors
Our NCSC‑certified assessors provide expert guidance throughout certification.
Certify on GuardNest
Complete your questionnaire on our platform, with built-in guidance, pre-submission checks and fast marking.
Simplified process
We handle the paperwork, coordinate technical testing and liaise with the certification body.
End-to-end support
From gap analysis to remediation, we get to know your systems and sector to provide practical advice.
Policy documentation
Get policy templates to back up your technical controls, giving you clear evidence for auditors and insurers.
Financial protection
Access to cyber insurance, with AXA handling the policy setup and communications once you're certified.
Why should you get certified?

Why should you get certified?
Why should you get certified?
92% fewer insurance claims are made by organisations with the Cyber Essentials controls in place.1
Protect against common cyber threats, including phishing, ransomware, and password attacks, by implementing technical controls.
Help meet key regulatory requirements, such as GDPR and the Data Protection Act 2018, by ensuring fundamental security controls are in place.
Open doors to government and public-sector contracts, where certification is often a mandatory requirement.
Demonstrate a commitment to cyber security, building trust with customers, suppliers, and stakeholders.
Cover straightforward yet effective technical controls that apply to organisations of any size or sector, regardless of dedicated IT resource or in-house expertise.
Cyber Essentials on GuardNest
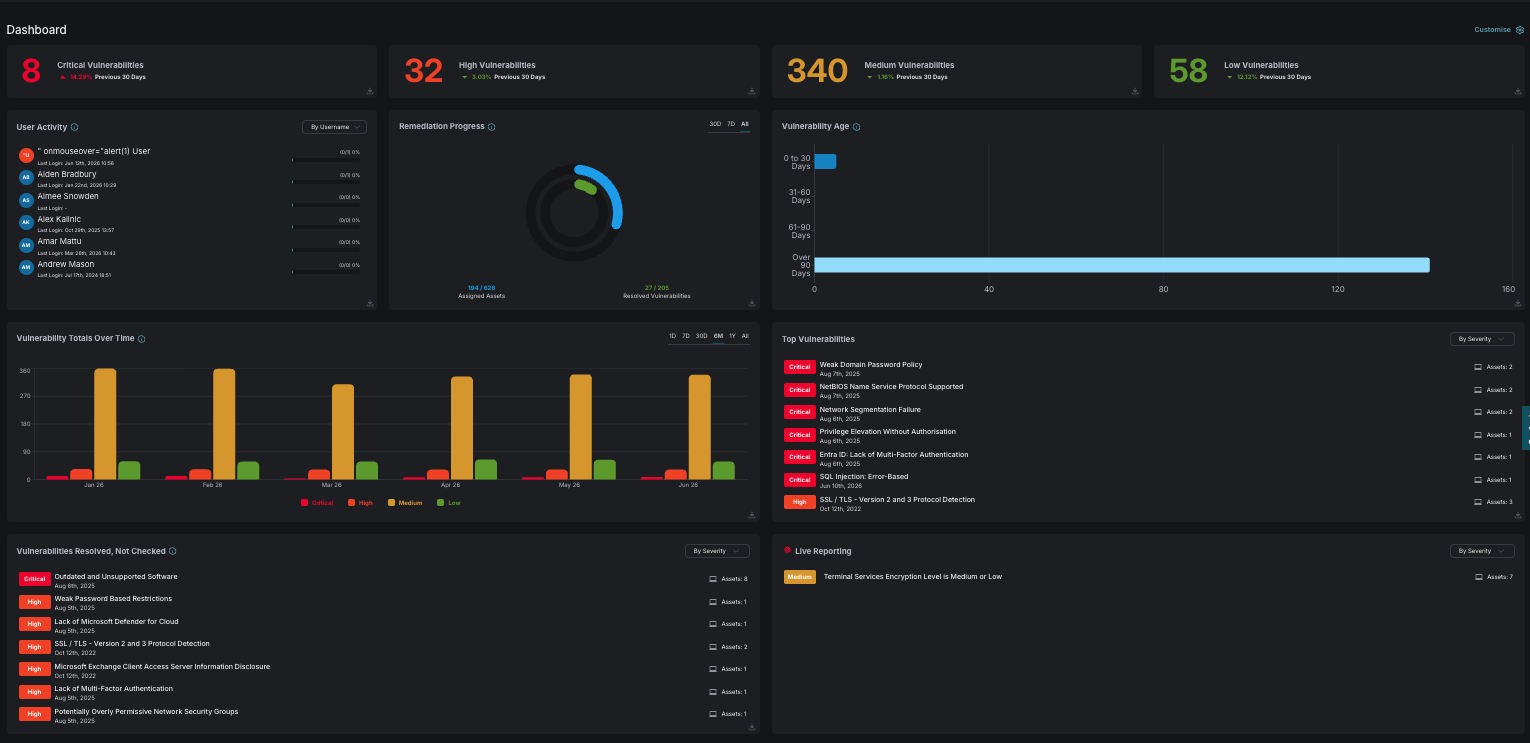
GuardNest is WorkNest's security platform for everything from Cyber Essentials and penetration testing to vulnerability scanning.
Likely issues, like out-of-support software or missing updates, are flagged as you go, so you can fix them before submitting.
Built-in tooltips explain what each question is asking, so fewer need to go to an assessor.
Get your questionnaire marked in as little as a few hours, so you know where you stand and can move on.
Your certificate, history and renewal reminders stay in GuardNest, so nothing depends on you remembering to check another system.
Assign questions to members of your team and leave comments to keep everyone updated.

The easiest route to certification is with consultant-led compliance support.
FAQs
After completing your Cyber Essentials or Cyber Essentials Plus assessment, you will receive:
An official PDF Cyber Essentials Certificate
A compliance report with all findings and recommendations
High-resolution Cyber Essentials logos and branding guidelines for use on your website and marketing materials
Your organisation will be listed on the Government website, showing your certification level
Our premium packages offer:
Additional free retests - Many organisations need at least one retest, and those with complex IT setups or still building their security posture often require two. Premium packages include up to 2 retests, saving time and money by eliminating the need to repurchase if more attempts are required.
Extended support time - Premium packages include up to 6 hours of expert guidance, ideal for organisations unfamiliar with the process who want extra time to elaborate on points and ask additional questions.
Tailored policy documents - Access pre-written policy templates, such as password and access control policies. These help organisations without existing policies meet Cyber Essentials requirements quickly and confidently, avoiding the time and complexity of drafting from scratch.
Cyber Essentials focuses on fundamental IT controls, whereas ISO 27001 takes a more holistic approach, incorporating policies and procedures. As ISO 27001 is much more involved, you’ll find it easier to obtain Cyber Essentials/Cyber Essentials Plus certification if you’re already ISO 27001 compliant.
We recommend achieving Cyber Essentials certification in addition to ISO 27001 as it demonstrates your commitment to good security practices, and some business/customers may only look for your Cyber Essentials certification, or not understand the difference between Cyber Essentials and ISO 27001.
| ISO 27001 | Cyber Essentials |
|---|---|---|
What is it | An international standard that sets out the requirements of an Information Security Management System to manage information security risk in a systematic way. The standard isn’t mandatory however many contracts/tenders do stipulate it as a requirement. | An NCSC backed UK assurance scheme addressing five technical security controls to help businesses address the most common cyber security vulnerabilities. Cyber Essentials is mandatory for government contracts. |
Risk | ISO 27001 adopts a risk-based approach where organisations set their risk acceptance criteria and risk methodology. This determines how risks are addressed. | Cyber Essentials aims to address the most common vulnerabilities found in organisations. It is not a risk-based approach. |
Recognition | ISO 27001 is an international standard recognised around the world. | Cyber Essentials is a UK based scheme and is not well known worldwide. |
Time to implement | Months | Days – weeks |
Certification process | Certification is provided by a Certification Body. This involves a Stage 1 and Stage 2 audit, and annual surveillance audits. Certification lasts for 3 years, as long as the organisation passes the audits. | Complete a self-assessment questionnaire (or undergo vulnerability scans and a workstation assessment if taking Cyber Essentials Plus) and be assessed by a IASME Cyber Essentials Assessor. Certification must be repeated annually. |
Costs | Med/High | Low |
Scope | Scope is defined by the organisation but the standard encompasses the business and is not just focused on IT. | Focuses on 5 key areas (shown below) and is more IT focused.
|
Applicability | Aimed at all businesses. | Aimed at all businesses, but particularly targets smaller businesses that may have not previously considered cyber security. |
Yes, all questions apply to applicants. Requirements may vary based on whether your organisation is office-based, hybrid or remote. ISP (Internet Service Provider) is not included in the scope. If no in-scope network exists, confirmation of software-based firewall use is required.
Yes, all questions presented in Cyber Essentials are applicable whether you are a single-person company or an organisation with 200+ employees. When answering those questions, consider the “what if?” scenarios.
Yes, you must use separate administrator accounts from standard user accounts, such as when installing software. Using administrator accounts all day exposes the device to malware compromise.
The inclusion of out-of-support or end-of-life operating systems in the scope of assessment will not be compliant with Cyber Essentials. However, you may still use unsupported operating systems if they are removed from the scope of assessment by isolating the device or OS from the organisation’s network via a segregated subset.
Danzell is the name for the updated Cyber Essentials requirements (v3.3), which came into effect on 27 April 2026. The five core controls haven't changed, but the assessment is now stricter in a few key areas:
MFA must be switched on for all cloud services where it's available, even if there's an extra cost, for every user, not just admins. Skipping this now means an automatic fail.
High-risk and critical security updates must be applied within 14 days, covering operating systems, applications, and router or firewall firmware. Missing this window is also an automatic fail rather than a note.
Scoping rules are tighter. If you're excluding any part of your cloud setup from the assessment, you'll need to explain why.
Cyber Essentials Plus checks have been tightened too, including how retesting works when issues are found on sampled devices.
If you're not sure how these changes affect your current setup, get in touch with us today and we'll walk you through it.

What our clients say
We’ve always been very impressed with the cyber security services WorkNest provide us. Their professional approach, knowledge and flexibility have ensured they have become a key trusted partner in our supply chain.

Paymentsense
Founder
WorkNest Secure delivered a highly professional and thorough incident response service. Their team’s technical knowledge, attention to detail, and clear communication throughout the process made a complex area easy to navigate. The quality of the analysis and final reporting gave us real assurance and added value to our internal security efforts, minimising the impact to the business.
Shoezone
Head of IT
We offer a comprehensive range of information security services, providing the strategy, governance, and hands-on expertise your organisation needs to stay secure and resilient.

Evaluate your systems, policies, and procedures to provide a holistic view of your cyber risk.
Get access to security expertise for strategy, risk management, and compliance.

Get effective SOC 2 compliance support from experienced consultants.
Simplify DORA compliance, with expert guidance, resilience strategies, and end-to-end support.

Receive end-to-end support for achieving and maintaining PCI DSS certification.